Who builds OPEREX

We come from operations. We build like engineers.

We are a small, senior team with backgrounds in chemical-plant operations, enterprise IT and software architecture. Every critical area has a named owner, and the key roles have a designated deputy — OPEREX does not rest on one person’s knowledge.

  • 10+ years in chemical-industry operations
  • ~10 years in enterprise IT and OT
  • Designated deputy with emergency access set out in writing

What we build

For industrial plants — primarily continuous-process, hazardous facilities — we build a system for operational excellence: from the shift log to reporting, with an auditable trail at every step.

Module by module

Switch on only what is needed

No forced bundles: pricing and rollout follow the modules, with a custom quote.

One shared foundation

Not separate islands

The modules build on the same shift log: what is recorded once is visible to the other modules.

Deployment

EU cloud or on site

A shared cloud operated in the EU (Germany) — or a dedicated, even air-gapped, on-premise deployment.

The team

Operations, IT and software-engineering knowledge in one team — every key area has a named owner.

Leadership

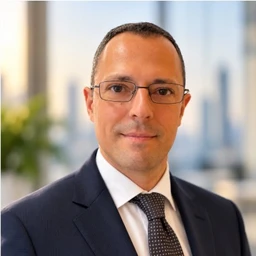
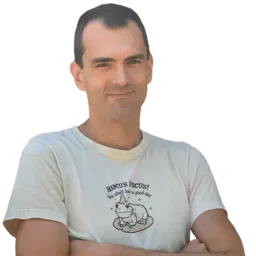
János Mészáros
Founder · product and industrial operations

János Mészáros

Chartered chemical engineer. More than a decade in chemical-industry operations — including as a plant manager, focused on optimisation and safe operation. “I ran the plant I now build for.”

Responsible for
  • product direction and the industrial domain content
  • information security (the designated responsible person)
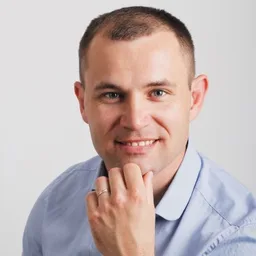
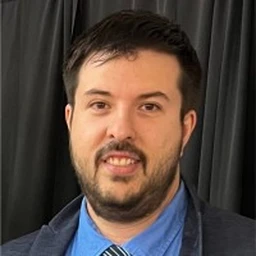
Tamás Gál
Software architect · engineering lead

Tamás Gál

Computer engineer (Óbuda University, 2013). A software developer since 2012; since 2020 the chief technology officer (CTO) of Florida-based EdgeServ POS, with experience in commercial POS systems.

Responsible for
  • software architecture and technical decisions
  • continuity of development
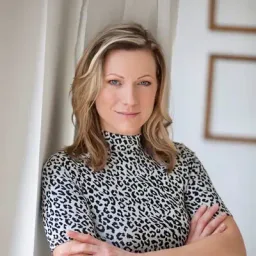
Réka Erdei
IT governance and business continuity

Réka Erdei

IT business consultant, business analyst and digital-transformation specialist — ~10 years running the IT systems of large companies, integrating enterprise IT with plant-floor operations (OT), and turning business requirements into specifications. MSc Chemical Engineering (BME).

Responsible for
  • IT governance and OT-integration considerations
  • designated deputy with emergency access to every system

Advisors

Sándor Kovács
Industrial operations

Sándor Kovács

A graduate of the Budapest University of Technology and Economics (BME). For more than 20 years he has led complex industrial plants in refining, gas-processing and petrochemical environments — currently responsible for plant reliability and operational discipline at ORYX GTL in Qatar.

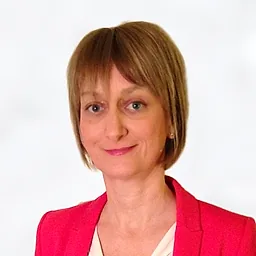
Beáta Horváth
HSE expert · permit to work

Beáta Horváth

Independent HSE consultant at Anzenta. Her work spans risk assessment, high-risk activities and industrial hygiene, lockout/tagout, machine-safety assessment, fire and construction-site safety, EHS audits and training — the field practice behind the permit-to-work module.

László Ökrös
Go-to-market and positioning

László Ökrös

Marketing advisor with a broad engineering background — bringing go-to-market and positioning to a product built by engineers.

How we work

We lead the product from the operations side; development runs as a team, in an agile framework, with modern practice. Architecture decisions, operating procedures and security policies live in writing, under version control — not in someone’s head.

Roles

Not in one pair of hands

Development, approval and production release are not in a single person’s hands.

Automated gates

Before every release

Automated tests and checks gate every deployment — we verify the gates by deliberately breaking things, to prove they really flag a fault.

Release and rollback

Test first, then production

Production runs on a separate machine with separate secrets, and only receives a release that has already passed the test environment; a failed deployment rolls back automatically.

Security by design

Not bolted on afterwards

Tenant isolation on every database row, an append-only audit trail, secrets never in the code, static security audit. Security →

Operations and vulnerabilities

Monitored, documented

External uptime monitoring every five minutes, written vulnerability and incident handling, mapped to all ten points of NIS2 Article 21(2). NIS2 →
Who is responsible for what

For procurement and supplier due diligence: every critical area has a name.

AreaOwner
Product and industrial domain contentJános Mészáros
Information securityJános Mészárosdeputy: Réka Erdei
Operations and emergency accessJános Mészárosdeputy with emergency access: Réka Erdei
IT governance, OT integrationRéka Erdeideputy: Tamás Gál
Software architecture, technical decisionsTamás Gáldeputy: János Mészáros
Permit to work: HSE content and validationBeáta Horváth
Go-to-marketLászló Ökrös
Operational practice, domain validationSándor Kovácsand Réka Erdei

We hand over the detailed role and access arrangements in our questionnaire pack, on request — the mapping is on the NIS2 page, the controls on the Security page.

It does not depend on one person

The question rightly asked of a supplier to a hazardous plant: what happens if someone drops out?

Deputising

A designated emergency-access holder

A written emergency-access procedure: sealed access, a recovery guide, and a drill repeated every six months.

Backup

One that actually restores

Encrypted off-server backups every 6 hours. We measure the restore, we do not assume it.

Exit

The data belongs to the plant

A full data export on request, followed by certified deletion — with the checksum of the export handed over.

No lock-in

We do not tie customers to us

Built on open standards (Postgres, S3-compatible storage); a packaged on-premise deployment for enterprise — the data never leaves the site.

Stated limits

What we do not claim yet

There is no independent external penetration test and no automatic failover yet — the “What we are still working on” section of the Security page shows the current state.

Company details and corporate contact

Company details

OPEREX

Registered seat: Diósd, Hungary · Data storage: EU (Germany).
Legal notice →

Procurement and security

support@operex.eu

Security questionnaire, data processing agreement, supplier due diligence — we send our questionnaire pack on request. Reporting a vulnerability: security@operex.eu · Security → · NIS2 →

Let's start a pilot

We'll show you OPEREX on your own operational processes — no strings attached.

Request a demo
Newsletter

Follow how OPEREX evolves

New modules, industrial shift-log tips and ISO 45001 practices — once a month at most, no spam.

You can unsubscribe anytime — the link is at the bottom of every email.